VDR & VER
Adopt the vulnerability detection, response, evaluation, and reporting rules.
For existing FedRAMP Rev5 providers
Manage vulnerabilities, maintain your certification package, and share the evidence agencies and assessors need. Put the Consolidated Rules into practice with Boundera.
Adopt the vulnerability detection, response, evaluation, and reporting rules.
Certification and assessment, cryptographic module use, incident communication, and significant changes.
The extension requires a corrective action plan that includes notice to all agencies.
VDR/VER: existing providers unable to meet December 7 may maintain certification through March 7 under a corrective action plan that includes agency notification. March 7 is specific to VDR/VER. Read the adoption notice.
The January rules have separate grace periods: June 1, 2027 for cryptographic module use, incident communication, and significant changes; the first FedRAMP independent assessment started after January 1 for certification, independent verification and validation, and minimum assessment scope.
Other requirements, including package formats and certification data sharing, phase in later in 2027. Check the full schedule for your program.
01 / Manage vulnerabilities
Scanner findings pile up across tools and tickets. Evaluating each one, tracking the response, and rebuilding reports by hand takes time away from resolving the risk.
Bring findings and service context together. Review findings in batches, stage evaluation and response instructions, and retain the evidence behind your team’s decisions.
Vulnerability Detail Report, Accepted Vulnerability Info, and Historical VER Activity, backed by maintained evaluation and response records.
AWS Inspector · public-api · High source severity
Reachable · Likely exploitable · N4 agency impact
Infrastructure team · Planned · Validation pending
Finding + evaluation + response history
02 / SSP to SDR
SSP narratives, control evidence, and assessment records drift apart. Each package update becomes another round of gathering documents and reconciling what changed.
Import supported SSP content, inspect the source behind each proposal, and approve what belongs in your control and rule records. Connect evidence, resolve gaps, and prepare your SDR and certification package from the work your team maintains.
Export the Security Decision Record and CPO in JSON and human-readable HTML, alongside ongoing certification and supporting reports.
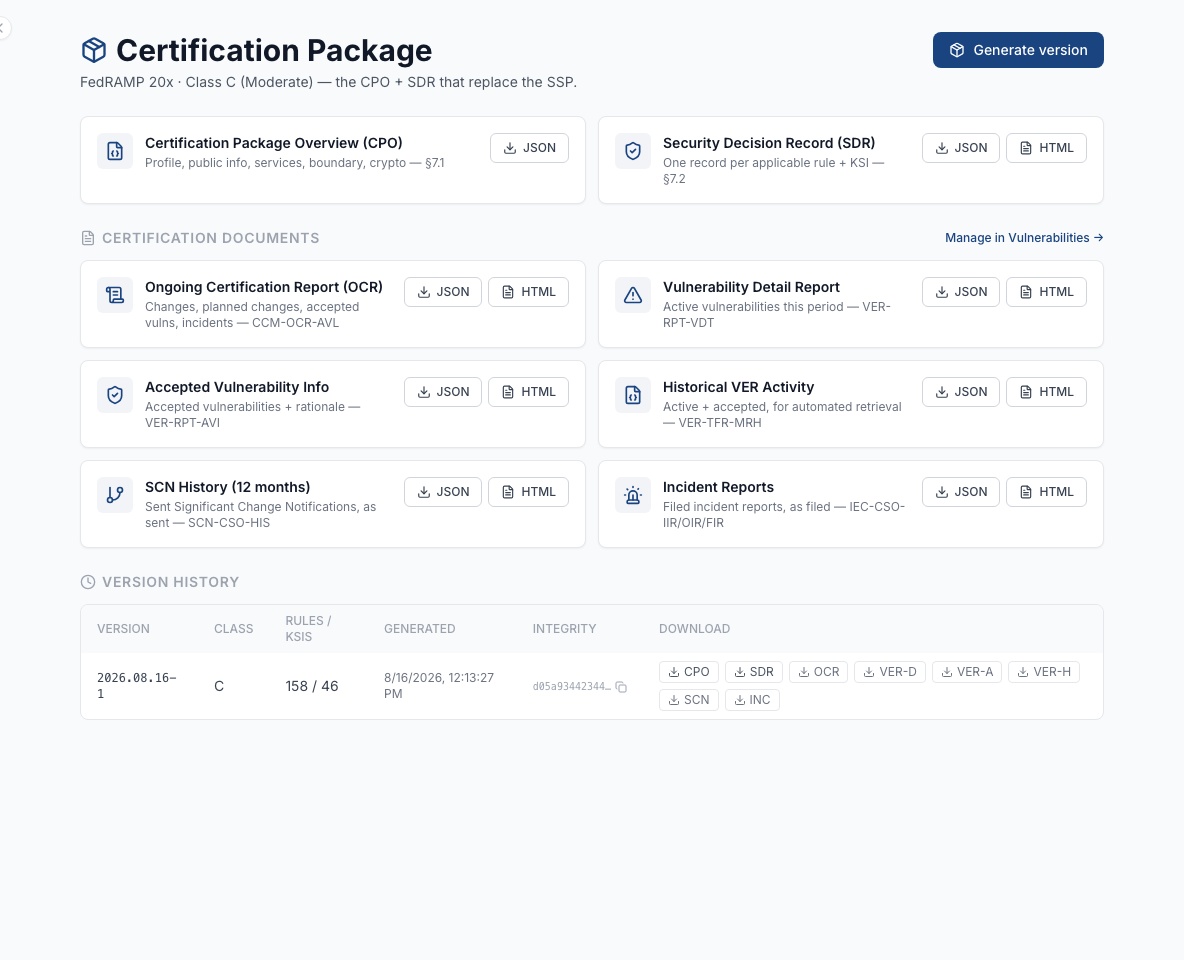
03 / Share your package
Evidence gets scattered across attachments and folders. Reviewers ask for the same records again, while your team tracks which version they received and who still needs access.
Share certification data through a Trust Center with controlled access. Give assessors a dedicated workspace for evidence requests and review records, and keep the supporting artifacts connected to your package.
An access-controlled Trust Center, linked certification documents and evidence, an assessor workspace, and a sharing audit trail.
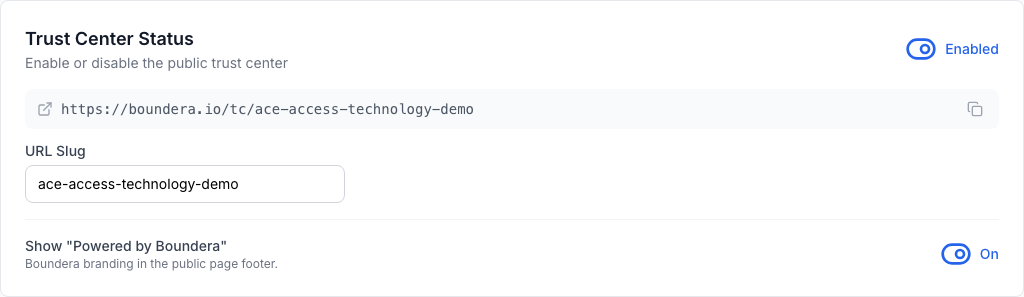
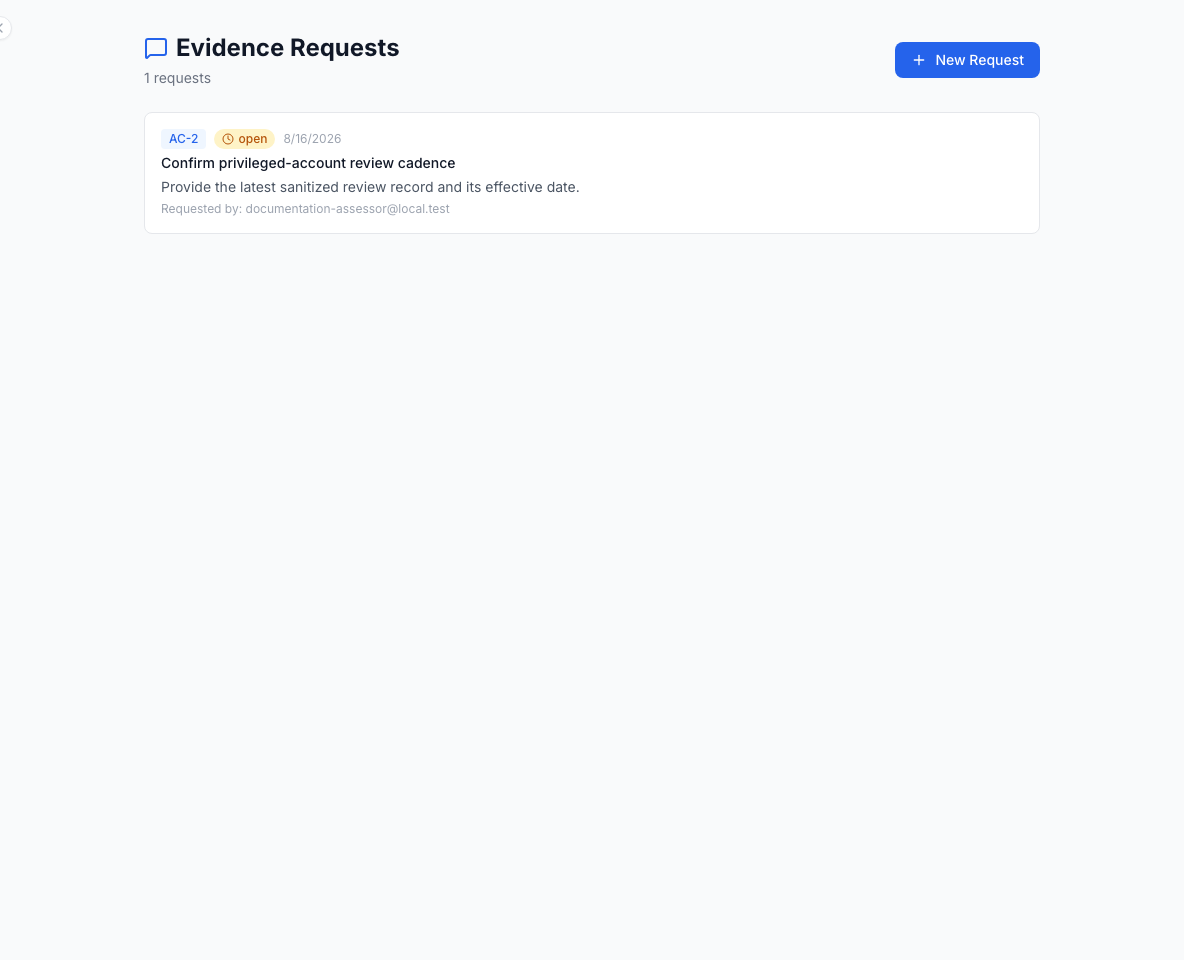
Product-guide screenshots with demo data.
Build on your existing environment
Start with the tools your team already uses. Map where findings come from, who owns each decision, and how remediation moves forward.
Findings, affected resources, and supporting technical evidence.
Contextual decisions, response obligations, and maintained records.
Owners, agreed ticket contents, progress, and evidence of the outcome.
Review permitted fields, access, and record references with your security team. Connector availability and custom ticketing work are confirmed for your deployment.
Start with VDR and VER. Add Consolidated Rules workflows, then KSI validation. Each annual plan includes the one before it.
A fit for your security boundary
Review hosting, access, AI processing, and retention before connecting your environment. Choose the deployment model that fits your team’s requirements.
AI context goes to your provider. See our privacy policy for processing and retention.
Before you get started
Yes. This page focuses on providers maintaining an existing FedRAMP Rev5 certification while adopting the Consolidated Rules for 2026. The rules have a phased adoption schedule; adopting them does not change your certification type. See the Rev5 schedule.
Your existing SSP and control work are the starting point. Boundera can import supported content into reviewable records, connect implementation details with evidence, and help prepare the certification package. Your team reviews what carries forward and resolves the gaps.
Start with your existing environment. During a walkthrough, we map supported finding sources, record ownership, and remediation handoffs. Connector coverage, permitted ticket fields, and any custom integration are confirmed against your deployment.
Your team still owns its security decisions, external communications, and submissions. Boundera supports evidence preparation, controlled sharing, and assessor collaboration. Independent assessment and the FedRAMP certification decision remain with the responsible parties.
Bring your current workflow or SSP. We’ll map the upcoming requirements to your finding sources, package records, and review process.
Plan your Rev5 transition